

-
Comprehensive Privacy and Cybersecurity Practice
Global co-chair of Wilson Sonsini’s data, privacy, and cybersecurity practice, Cédric provides strategic counseling on the GDPR and global data regulations, from product development and compliance programs to international growth.
-
Represents Companies in High-Stakes Incidents and Complex Regulatory Matters
Cédric guides companies through high-stakes investigations by EU data protection authorities and the European Commission, cybersecurity incidents, and related litigation, coordinating regulatory responses across jurisdictions.
-
AI Compliance Experience
Cédric advises leading AI developers on EU AI Act compliance and engagement with the European Commission’s AI Office, including model reporting, systemic-risk obligations, and regulatory inquiries.
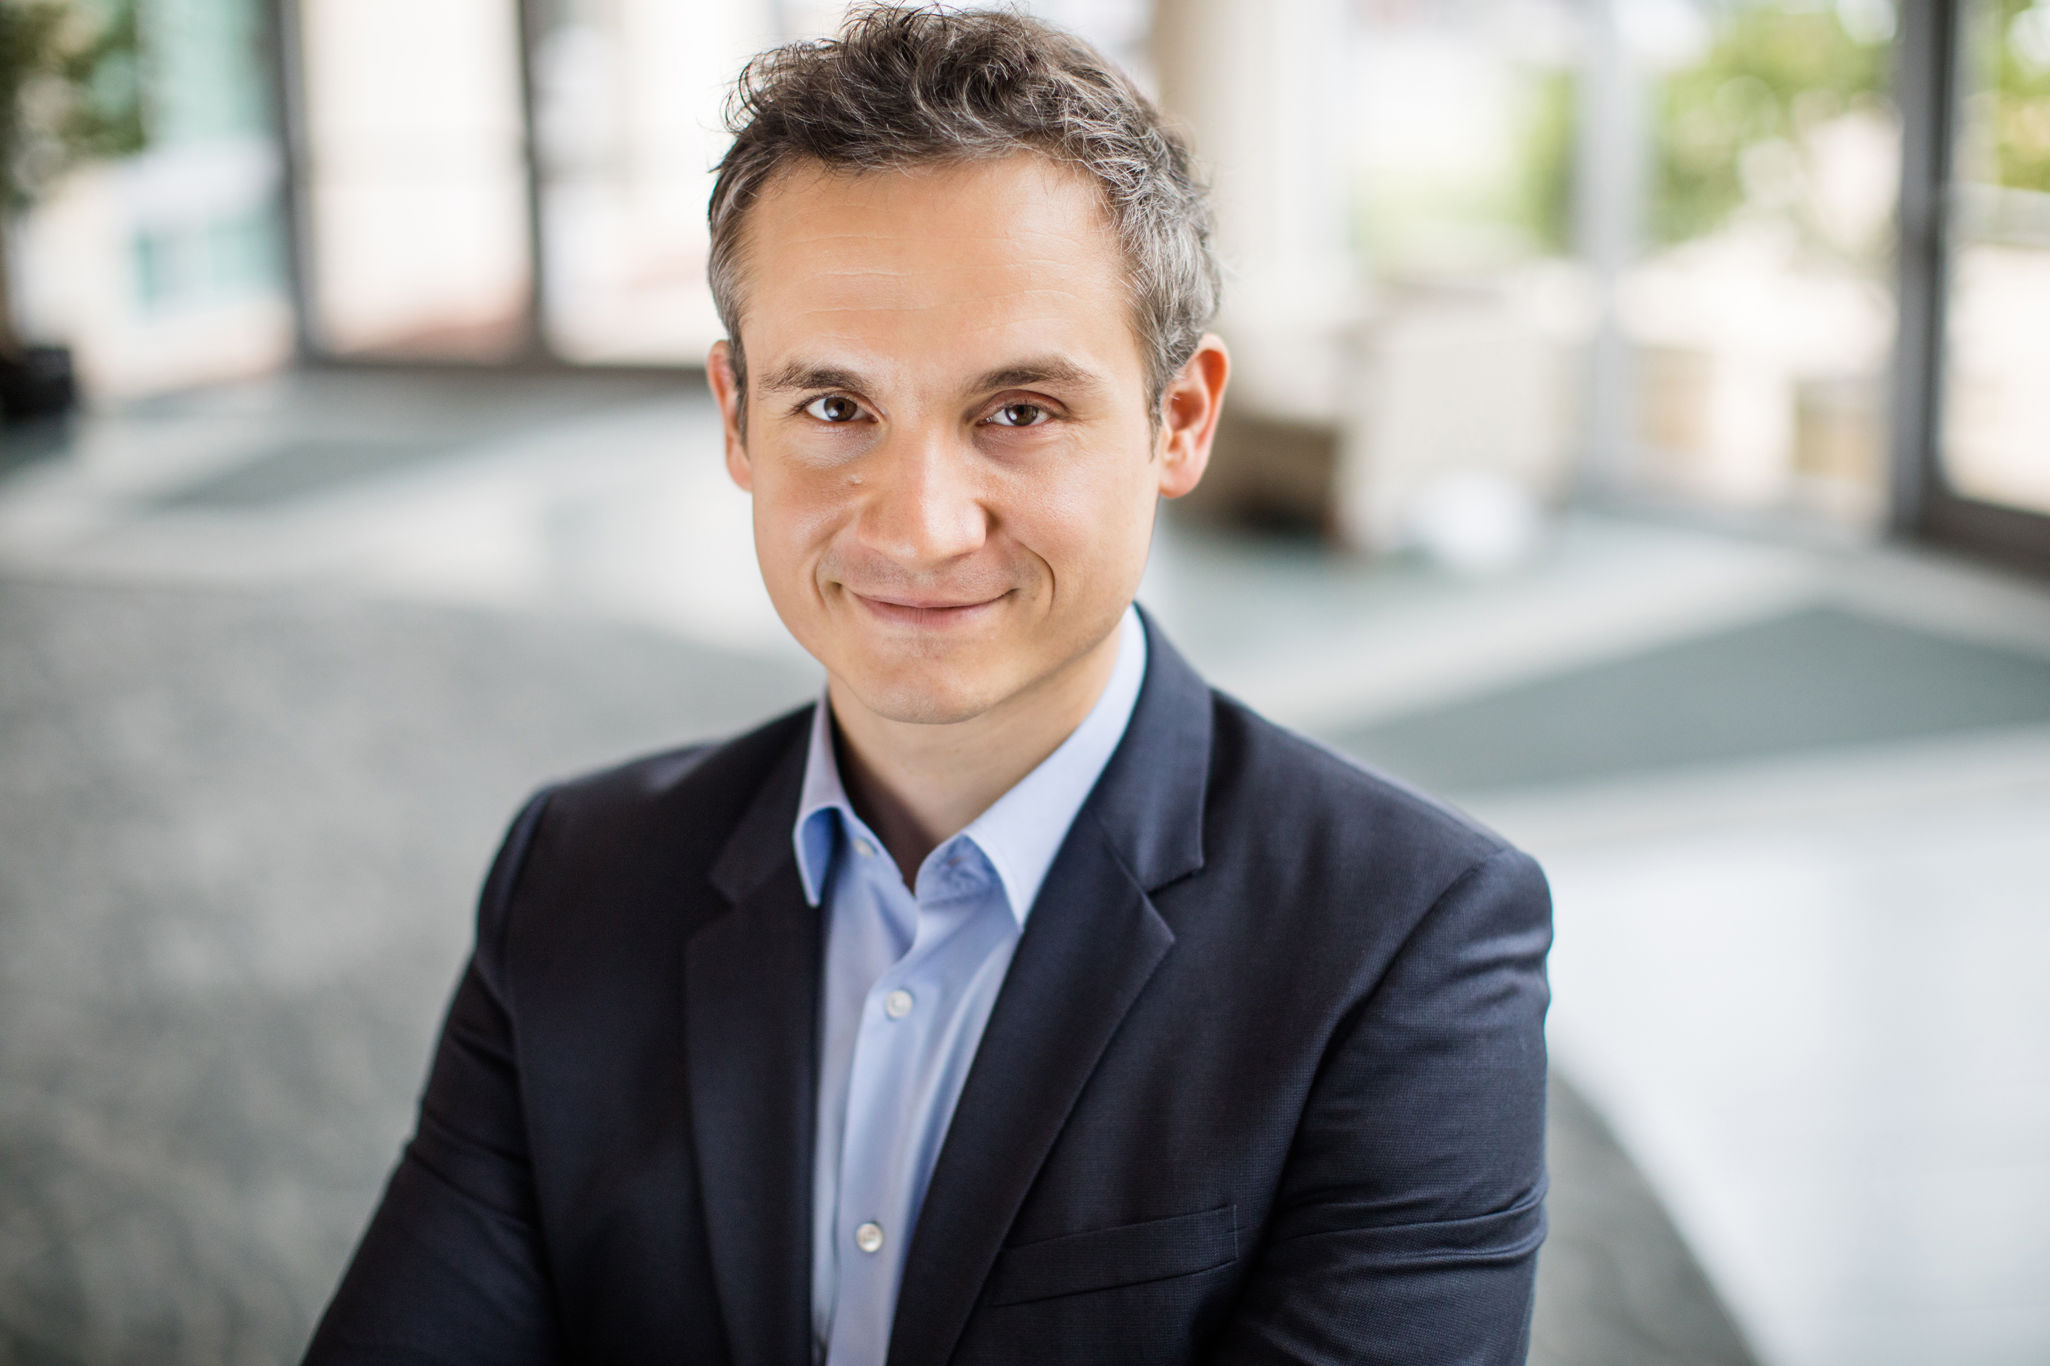
Cédric Burton co-chairs Wilson Sonsini's global data, privacy, and cybersecurity practice, leads the EU data regulatory practice, is the managing partner of the firm's Brussels office, and is a previous member of the firm's board of directors.
Cédric has 20 years of experience advising technology companies on privacy, data protection, and cybersecurity. His practice combines regulatory investigations and enforcement defense, global counseling on data and digital regulations, and cybersecurity incident response. He helps clients navigate overlapping legal requirements and regulators' enforcement priorities while supporting product development and international growth.
Cédric represents companies in high-stakes regulatory investigations and proceedings before European data protection authorities and the European Commission, including its AI Office. His work spans the General Data Protection Regulation (GDPR), the EU Artificial Intelligence Act (AI Act), and broader data regulation. He coordinates cross-border defense strategies, including responses to parallel inquiries, requests for information, on-site inspections, and sanction proceedings. Working with local counsel where appropriate, he advises on challenges to regulatory fines and other enforcement measures and maintains a consistent approach across jurisdictions.
He serves as lead global privacy and data protection counsel to multinational companies and coordinates broader advice on AI, data protection, cybersecurity, and digital regulation. His counseling covers product launches, international expansion, data use and sharing, cross-border transfers, governance, and compliance programs, working to reconcile requirements across jurisdictions.
Cédric advises providers of general-purpose AI models, including models with systemic risk, on the EU AI Act and the General-Purpose AI Code of Practice. His work covers topics such as safety and security model reports, serious incident reporting, independent evaluator access, transparency and training-content summaries, and engagement with the EC’s AI Office. He also advises on the classification of AI models and systems and on AI governance and compliance frameworks.
Cédric advises on privacy and data protection issues arising in the development and launch of generative and agentic AI products. His work covers model training and web scraping, personalization, age assurance and children’s privacy, and the processing of sensitive personal data.
Cédric guides companies through complex cross-border cybersecurity incidents, including data breaches and ransomware attacks. His practice covers regulatory notifications, coordination of forensic investigations and remediation, engagement with regulators and law enforcement, and follow-on regulatory investigations. He works with litigation counsel on related civil claims and advises on incident preparedness, including response plans, ransomware playbooks, and tabletop exercises. He also advises on cybersecurity requirements under NIS2, the Digital Operational Resilience Act (DORA), and the EU Cyber Resilience Act.
He regularly advises clients on:
- Multijurisdictional regulatory investigations, including coordinating litigation before national courts and the European Court of Justice;
- Complying with the GDPR and other data regulatory requirements;
- Creating and implementing global compliance programs;
- Advising on main establishment, the one-stop-shop, and regulatory engagement strategies;
- Defining international data transfer strategies, including binding corporate rules and transfer impact assessments;
- Advising on anonymization, pseudonymization, and privacy-enhancing technologies;
- Planning for and managing data breaches and cybersecurity incidents;
- Advising on data protection issues in the context of mergers, acquisitions, and other commercial transactions; and
- Negotiating data processing agreements.
His counseling extends across the EU’s data and digital regulatory framework, including requirements governing artificial intelligence, data access and use, digital platforms, and cybersecurity. His advice covers:
- Artificial Intelligence Act (AI Act);
- Data protection issues related to the Digital Markets Act (DMA) and the Digital Services Act (DSA);
- NIS2 Directive;
- Data Act (DA);
- Digital Operational Resilience Act (DORA);
- Cyber Resilience Act (CRA);
- Data Governance Act (DGA); and
- Data protection aspects of the second Payment Services Directive (PSD2).
Cédric’s advice addresses both the requirements of individual regulatory regimes and their interaction with the GDPR. He helps clients develop coordinated compliance strategies and manage regulatory engagement across overlapping legal frameworks.
Clients praise Cédric for his pragmatic approach and describe him as a lawyer who is “sensitive to political issues and honest in his perception of risk” (Chambers Europe).
Cédric has authored many articles relating to privacy and data protection law and regularly speaks on AI and data protection-related topics. His work has been recognized by Who's Who Legal Thought Leaders, Chambers Europe, Legal 500, BTI Consulting, and Law360.
Earlier in his career, Cédric was an associate in the Brussels office of Hunton & Williams. Before that, he worked as a research fellow in privacy and data protection law at the Research Center on IT and Law (CRID) of the University of Namur (Belgium), as well as the Center on Law and Information Policy (CLIP) at Fordham University (New York). Cédric is fluent in French and English.
- LL.M., Intellectual Property and Information Technology Law, Fordham University School of Law, 2007
- LL.M., IT Laws and Management, University of Namur, Belgium, 2005Magna Cum Laude; Recipient, "Best Interdisciplinary Student Award," 2005; Recipient, "Best Brief Prize" as winner of International Moot Cyber-Tribunal Contest, 2005
- J.D., University of Liège, Belgium, 2004Cum Laude
- Law360’s 2022 Cybersecurity & Privacy Editorial Advisory Board
- International Association of Privacy Professionals (IAPP), 2007–present
- International Association of Privacy Professional (IAPP) European Advisory Board, 2015–2017
- Selected for inclusion in the 2024–2026 editions of the Lawdragon’s 500 Leading Global Cyber Lawyers guide
- Selected for inclusion in the 2024 edition of the Global Data Review 100
- Recognized in the 2018–2026 editions of Chambers Europe for TMT: Data Protection - Belgium
- Recognized as a leading individual and in Tier 1 in privacy and data protection law by Legal 500, 2018–2024
- Listed in the Who's Who Legal Thought Leaders, 2019–2022
- Recognized among the leading "Privacy and Data Security Lawyers" in Belgium by Best Lawyers, 2019–2022
- Selected for inclusion in Law360’s 2019 list of "Top Attorneys Under 40" in the cybersecurity and privacy category
- Selected for inclusion in 2014–2015 of The Legal 500 Europe, Belgium, Privacy & Data Protection
- Selected for inclusion in The Who's Who Legal Telecommunications Media & Technology, Information Technology, 2014–2015
- Recognized as a "leading talent" in privacy and data protection law in The International Who's Who of Information Technology Lawyers, 2013
- Recognized as a leader in his field and ranked as an "Associate to Watch" in the 2012 and 2013 editions of Chambers Europe – TMT, Information Technology, Belgium
- Brussels Bar
Select Regulatory Investigations and Litigation Matters
- Represented OpenAI, working alongside Italian counsel Chiomenti, in its successful appeal against an Italian data protection enforcement decision. In March 2026, the Court of Rome annulled the €15 million fine and the requirement to conduct an information campaign about AI model training.
- Coordinates a leading AI developer’s responses to parallel data protection investigations in Europe and other regions, including requests for information, on-site inspections, sanction proceedings, and related court challenges.
- Advises a leading AI developer on its response to a European Commission AI Office request for information concerning model security.
- Advises companies on responses to European Commission AI Office requests for information concerning copyright compliance under the EU AI Act.
- Advises a leading AI developer on incident-related engagement with the European Commission’s AI Office.
- Advised technology companies on Irish Data Protection Commission inquiries concerning account creation, consent, personalization, transparency, and cookies, including cross-border cooperation under Article 60 GDPR.
- Represents a financial services company in a pan-European investigation concerning the use of biometric identification for anti-money laundering and fraud prevention.
- Represented a social network in investigations by EU supervisory authorities in various countries, including Germany, Italy, the Netherlands, France, and Denmark, and a European Data Protection Board task force.
- Advised a social network in relation to Article 66 GDPR proceedings.
- Represents a service provider in a supervisory authority inquiry related to fraud products and services.
- Represented a leading social network in a CNIL investigation concerning cookies compliance.
- Advised an audio streaming company in regulatory inquiries concerning cookies compliance.
- Advised an online social platform on responding to ICO inquiries related to a data breach and its compliance with age-appropriate design requirements.
- Represented a car manufacturer in relation to an investigation into its data location practices.
- Represented a drone manufacturer in relation to inquiries from EU data protection authorities.
- Advised a large public multinational company on an investigation by the Spanish supervisory authority.
Select Counseling Matters
- Acts as lead global data protection counsel for Mastercard, advising on privacy compliance worldwide and the rollout of new products and services. His work has also included advising on the integration of Recorded Future.
- Advises a leading provider of general-purpose AI models on safety and security model reports, serious incident reporting, and independent evaluator access under the EU AI Act and General-Purpose AI Code of Practice.
- Advises a general-purpose AI model developer on regulatory classification, technical documentation, downstream-provider information, copyright policies, training-content summaries, and AI governance.
- Advises a leading global technology company on strategic data protection and privacy issues arising out of data-related rules in the EU, such as the Digital Markets Act, the Digital Services Act, and the reform of consumer protection laws.
- Advises hundreds of companies on GDPR compliance and international data transfers, including standard contractual clauses, binding corporate rules, and transfer impact assessments. His experience also includes Safe Harbor and Privacy Shield certifications before their invalidation by the CJEU.
- Advises an e-commerce company on strategic data protection and privacy issues, including risks and benefits of data localization and GDPR's data transfer rules, the EU-U.S. Data Privacy Framework, and the data protection impact of the Digital Markets Act.
- Advises a SaaS company that provides self-optimizing and smart WiFi services on GDPR compliance, including drafting its privacy policy, reviewing user registration flow, preparing and negotiating data processing agreements, assisting with the creation and implementation of various policies and procedures, advising on data transfer restrictions and the implementation of data transfer agreements, and advising on the use of cookies and similar technologies.
- Acts as lead global privacy counsel for a financial messaging provider, advising on GDPR compliance, governance, data transfers, contracts, data subject rights, and cooperation with supervisory authorities.
- Advises a leading social network on various strategic aspects of its data protection compliance program, including cookie rules, data transfers, accountability obligations, and the one-stop-shop.
- Advises a SaaS company on its rollout of a smart security camera under GDPR, U.S. law, and local laws in Belgium, Germany, the UK, Canada, and the Netherlands.
- Acts as lead privacy counsel for a multinational beverage company on international privacy compliance, including the preparation of binding corporate rules and support through the regulatory approval process, incident response, the Data Protection Officer function, data subject rights, and engagement with supervisory authorities.
- Advised a provider of privacy-enhancing technologies on GDPR compliance and the design of anonymization products and services.
- Advised digital health and life sciences companies on health-data processing, including privacy notices, informed consent, privacy by design, data transfers, anonymization, and pseudonymization.
- Advised a leading electric car manufacturer on its GDPR compliance program, including its privacy policy, accountability requirements, pseudonymization, and anonymization practices.
- Advises a leading audio media service company on GDPR compliance, including privacy policy, data processing agreements, the implementation of the ePrivacy Directive and cookie rules, data retention, data anonymization, international data transfers, and incident responses.
- Advises an electric car manufacturer on its GDPR compliance program, including on a data transfer strategy, data processing agreements, marketing requirements, handling individuals' rights, and complying with notice and consent obligations.
- Advises an online marketplace on its GDPR compliance program, including data transfer issues, replying to individuals' requests to exercise their rights, incident responses, and accountability obligations.
Select Cybersecurity and Incident Response Matters
- Advised a payment provider on a security incident and related regulatory investigations, forensic work, remediation, and civil litigation, including coordinating with local counsel on class actions in Germany.
- Advised a multinational B2B company on its response to a ransomware attack, including cross-border notification assessments and engagement with data protection and cybersecurity authorities.
Select Transactions
Advised on the data protection aspects of the following transactions:
- Mastercard on its agreement to acquire BVNK, including the data protection and cybersecurity aspects of the transaction.
- Mastercard’s acquisitions of several companies, including Baffin Bay, Dynamic Yield, Aiia, Ciphertrace, Finicity, Ekata, RiskRecon, and SessionM.
- Aurora on its acquisition of Uber ATG.
- WaveOptics on its sale to Snap.
Select Publications
-
Co-author, “EU-U.S. Data Transfer Ruling Offers Reassurance to Companies,” Law360, October 7, 2025
-
Co-author, “EDPB Issues First Guidelines on the Interplay Between the Digital Services Act and the GDPR,” Wilson Sonsini Alert, September 22, 2025
-
Co-author, “EU Court Upholds the Validity of the EU-U.S. Data Privacy Framework,” Wilson Sonsini Alert, September 3, 2025
- Co-author, “EU Reaches a Deal on Rules for Swifter Cross-Border GDPR Enforcement,” Wilson Sonsini Alert, June 17, 2025
- Co-author, “Regulators Target AI As Evolving Technology Threatens Fair Competition in Digital Economy,” GCR - Data & Antitrust Guide; Second Edition, May 30, 2025
-
Co-author, “Ransomware Attacks: UK Government Proposes Ransom Payment Ban and Mandatory Notification Requirements,” Wilson Sonsini Alert, January 24, 2025
- Co-author, “DORA: New EU Cybersecurity Requirements for the Financial Sector Enter into Force,” Wilson Sonsini Alert, January 17, 2025
- Co-author, “Increased Focus on the Protection of Minors and Age Verification in the EU and the UK,” Wilson Sonsini Alert, January 9, 2025
- Co-author, “EU Court Awards Damages for Breach of EU Data Transfer Rules,” Wilson Sonsini Alert, January 9, 2025
-
Co-author, “EU Privacy Regulators Confirm That Legitimate Interest Is a Valid Legal Basis for AI Model Training and Deployment,” Wilson Sonsini Alert, December 20, 2024
- Co-author, “New EU Cybersecurity Obligations for Connected Devices: What You Need to Know,” The WSGR Data Advisor, October 31, 2024
- Co-author, “Regulators in Europe Signal Increased Scrutiny of Online Platforms,” Wilson Sonsini Alert, October 21, 2024
- Co-author, “EU Agencies to Develop Guidance on the Interplay Between the DMA and GDPR,” Wilson Sonsini Alert, October 2, 2024
- Co-author, “Cybersecurity: A Critical Element in Your 2025 Business Forecast,” Wilson Sonsini Alert, September 30, 2024
- Co-author with T. Evans and H. Watson, “Making the Internet Safe for Children: Ofcom’s Latest Consultation,” PLC Magazine, June 3, 2024
- Co-author, “French Data Protection Authority Publishes Recommendations on the Development of AI Systems: Seven Takeaways,” Wilson Sonsini Alert, April 23, 2024
- Co-author, “EU Court of Justice Landmark Ruling on Digital Advertising and GDPR Compliance,” Wilson Sonsini Alert, March 20, 2024
- Co-author, “10 Privacy Predictions in the EU for 2024,” Wilson Sonsini Alert, January 17, 2024
- Co-author, “EU Lawmakers Reach Political Agreement on the AI Act,” Wilson Sonsini Alert, December 11, 2023
- Co-author, “Flagship Online Safety Bill Moves Closer to Enactment in the UK: Who Will Be in Scope and What Will It Require?” Wilson Sonsini Alert, October 10, 2023
- Co-author, “UK-U.S. Data Bridge Commencement Date Announced,” Wilson Sonsini Alert, September 22, 2023
- Co-author, “EU and U.S. Finalize Data Privacy Framework: Here’s How to Get Certified,” Wilson Sonsini Alert, July 10, 2023
- Co-author, “EU Privacy Regulators Coordinate to Assess Compliance with the GDPR Rules on Data Protection Officers,” Wilson Sonsini Alert, March 17, 2023
- Co-author, “CJEU Finds That Companies Must Provide Individuals with the Identity of Data Recipients When Responding to Data Access Requests,” Wilson Sonsini Alert, January 27, 2023
- Co-author, “European Union Adopts Flagship Digital Services Act,” Wilson Sonsini Alert, October 31, 2022
- Co-author, “Formal Publication of the DMA and Timelines for Compliance,” Wilson Sonsini Alert, October 13, 2022
- Co-author, “EU to Open San Francisco Office to Advance Its Digital Regulation Agenda,” The WSGR Data Advisor, April 27, 2022
- Co-author, “EU Reaches Political Agreement on Additional New Rules for Digital Platforms in the Digital Services Act,” The WSGR Data Advisor, April 26, 2022
- Contributor, “Accountability to Data Subjects and Regulators,” The Guide to Data as a Critical Asset, Global Data Review, 2022
- Co-author, “EU Adopts New Rules to Significantly Limit the Power of Tech Platforms,” The WSGR Data Advisor, March 30, 2022
- Co-author, “Political Agreement on a New Framework for EU-U.S. Personal Data Transfers,” The WSGR Data Advisor, March 29, 2022
- Co-author, “EU Parliament and Council Take Next Steps to Advance Major New Rules for Digital Platforms,” The WSGR Data Advisor, February 25, 2022
- Co-author with L. Brodahl, C. Evrard, and A. Lépine, “Belgian DPA Finds That IAB Europe’s Cookie Consent Framework Violates the GDPR,” Wilson Sonsini Alert, February 8, 2022
- Co-author, “European Court of Justice Finds That 'Inbox Advertising' Is Direct Marketing,” The WSGR Data Advisor, December 6, 2021
- Co-author with L. De Boel, J. Dhont, and R. Fol, “EU Regulators Define Data Transfers,” Wilson Sonsini Alert, November 23, 2021
- Co-author, “European Commission Proposes New Rules for Digital Platforms,” Wilson Sonsini Alert, January 12, 2021
- Co-author, “EU Commission Publishes Proposal for e-Privacy Regulation: The Top Nine Key Points You Need to Know,” WSGR Alert, January 10, 2017
- Co-author, “EU Commission Publishes EU-U.S. Privacy Shield,” WSGR Alert, February 2016
- Co-author, “EU Data Protection Authorities Issue Statement Following Agreement on EU-U.S. Privacy Shield,” WSGR Alert, February 2016
- Co-author, “EU and U.S. Reach a Political Agreement on Transatlantic Data Transfer Deal,” WSGR Alert, February 2016
- Co-author, “Profile: European Union,” Bloomberg BNA, Privacy & Security Law Report, February 2016
- Co-author, “The Final European Union General Data Protection Regulation,” Bloomberg BNA, Privacy & Security Law Report, January 2016
- Co-author, “Political Agreement Reached for New EU Data Protection Regulation—Official Adoption Around the Corner,” WSGR Alert, December 2015
- Co-author, “What's Next for U.S.-EU Data Transfers? An Analysis of Recent Developments Following Schrems,” The WSGR Data Advisor, November 2015
- Co-author, “Landmark Decision Clarifies Territorial Scope of Application of National Data Protection Laws in the EU,” The WSGR Data Advisor, November 2015
- Author, “EU Data Protection Authorities Issue Statement Following Schrems Decision,” WSGR Alert, October 2015
- Co-author, “EU's Highest Court Declares Safe Harbor Invalid,” WSGR Alert, October 2015
- Co-author, “Advocate General Advises EU's Highest Court to Deem Safe Harbor Invalid and to Allow EU Data Protection Authorities to Suspend Data Transfers to the U.S.,” WSGR Alert, September 2015
- Co-author, “Personal Data, Anonymization, and Pseudonymization in the EU,” The WSGR Data Advisor, September 2015
- Co-author, “Status Update on the EU Data Protection Regulation,” The WSGR Data Advisor, July 2015
- Co-author, “The Proposed EU Data Protection Regulation Three Years Later: The Council Position,” Bloomberg BNA, Privacy & Security Law Report, June 2015
- Co-author, “EU Reaches Milestone Towards the Adoption of Revised Data Protection Framework,” WSGR Alert, June 2015
- Co-author, “French Data Protection Authority Unveils Its Inspection Program for 2015,” WSGR Alert, May 2015
- Co-author, “EU Data Protection Regulators Issue Guidance on the Internet of Things and Device Fingerprinting,” Eye on Privacy, February 2015
- Author, “Google Moves to Implement the 'Right to Be Forgotten,'” Data Protection Law & Policy, Volume 11, Issue 5, May 2014
Select Speaking Engagements
- Speaker, “Global Incident Response: Managing Incidents Impacting Global Enterprises,”, Incident Response Forum Europe 2024, October 17, 2024
- Speaker, “Managing the GDPR After a Data Breach,” Incident Response Forum Europe 2023, December 7, 2023
- Speaker, “Key Trends in Antitrust, Privacy, Cybersecurity, Sanctions and Foreign Direct Investment – Hong Kong, E.U., UK and US Perspectives,” Asian Academy of International Law and AAIL Foundation, June 5, 2023
- Panelist, “DMA, DSA, DA, DGA, AI Act: How to Navigate a Soup of new EU Data Regulations,” IAPP Europe Data Protection Congress 2022, November 16, 2022
- Speaker, “How To Redline SaaS MSAs And DPAs For In-House Counsel,” In-House Connect, October 12, 2022
- Panelist, “Managing the GDPR After a Data Breach,” Incident Response Forum Europe 2022, September 22, 2022
- Lecturer, “Data protection concerns in data-driven mergers and acquisitions,” VUB Summer School Academy, June 29, 2022
- Presenter, “EU's Digital Services Act (DSA) final text's data protection implications,” Future of Privacy Forum, June 22, 2022
- Panelist, “The EU Digital Single Market: implementation and implication,” GDR Connect: Regulation and Digital Strategy, May 11, 2022
-
Panelist, “Schrems II: The Practical Implications,” International Association of Privacy Professionals LinkedIn Live, July 20, 2020
- Presenter, “WSGR Getting Ready for the GDPR Series - Session 5: Regulatory Aspects of the GDPR,” WSGR Privacy & Data Protection Webcast, November 17, 2016
- Presenter, “WSGR Getting Ready for the GDPR Series - Session 4: The GDPR, Privacy Shield, and EU-U.S. Data Transfers - What to Do Now?,” WSGR Privacy & Data Protection Webcast, September 13, 2016
- Presenter, “WSGR Getting Ready for the GDPR Series - Session 3: The GDPR for Service Providers,” WSGR Privacy & Data Protection Webcast, July 12, 2016
- Presenter, “WSGR Getting Ready for the GDPR Series - Session 2: Enhanced Individuals Rights,” WSGR Privacy & Data Protection Webcast, June 8, 2016
- Presenter, “Getting Ready for the GDPR,” WSGR Privacy & Data Protection Webcast, May 2016
- Presenter, “The EU-U.S. Privacy Shield: A New Tool for Data Transfers to the U.S.?” WSGR Privacy & Data Protection Webcast, March 2016
- Panelist, “Transferts de données à caractère personnel intra-groupe et à l'international, quels risques encourus ? Comment être conforme ?” CREO Business Information & Seminars, Brussels, Belgium, February 2016
- Panelist, “General Data Protection Regulation,” Brussels European Employee Relations Group (BEERG), Brussels, Belgium, February 2016
- Presenter, “Update on the EU-U.S. Safe Harbor Program,” WSGR Privacy & Data Protection Webcast, October 2015
- Presenter, “An Update on the EU Data Protection Regulation,” WSGR Privacy & Data Protection Webcast, July 2015
- Panelist, “EU Data Protection Reform and Data Localization Initiatives: Impacts and Strategies for Global Data Transfers,” IAPP Europe Data Protection Congress 2014, Brussels, Belgium, November 2014
- Panelist, “Data-Driven Economy – How Can We Use the Full Potential of the Data-Driven Revolution?” TechAmerica Europe's Annual Plenary, November 2014
- Panelist, “Ethics, Fundamental Rights and Big Data,” 36th International Conference of Data Protection and Privacy Commissioners, Balaclava, Mauritius, October 2014
- Panelist, “Privacy in mobility and location data” panel, 7th International Conference, Computers, Privacy & Data Protection, Reforming Data Protection: The Global Perspective, Brussels, Belgium, January 2014